
From 0 to catastrophe, we stayed at zero. A 9.2 out of 10 risk shaking the internet, but not us.
On October 21, 2026, two critical security flaws in PHP were made public under the name “PHP2Shell”. PHP runs roughly 70% of all websites, from small business pages to most WordPress sites, and these flaws let an attacker take over a website’s server without a password. Security experts rated them 9.2 out of 10, and attackers had been trying them since October 17, days before any fix existed.
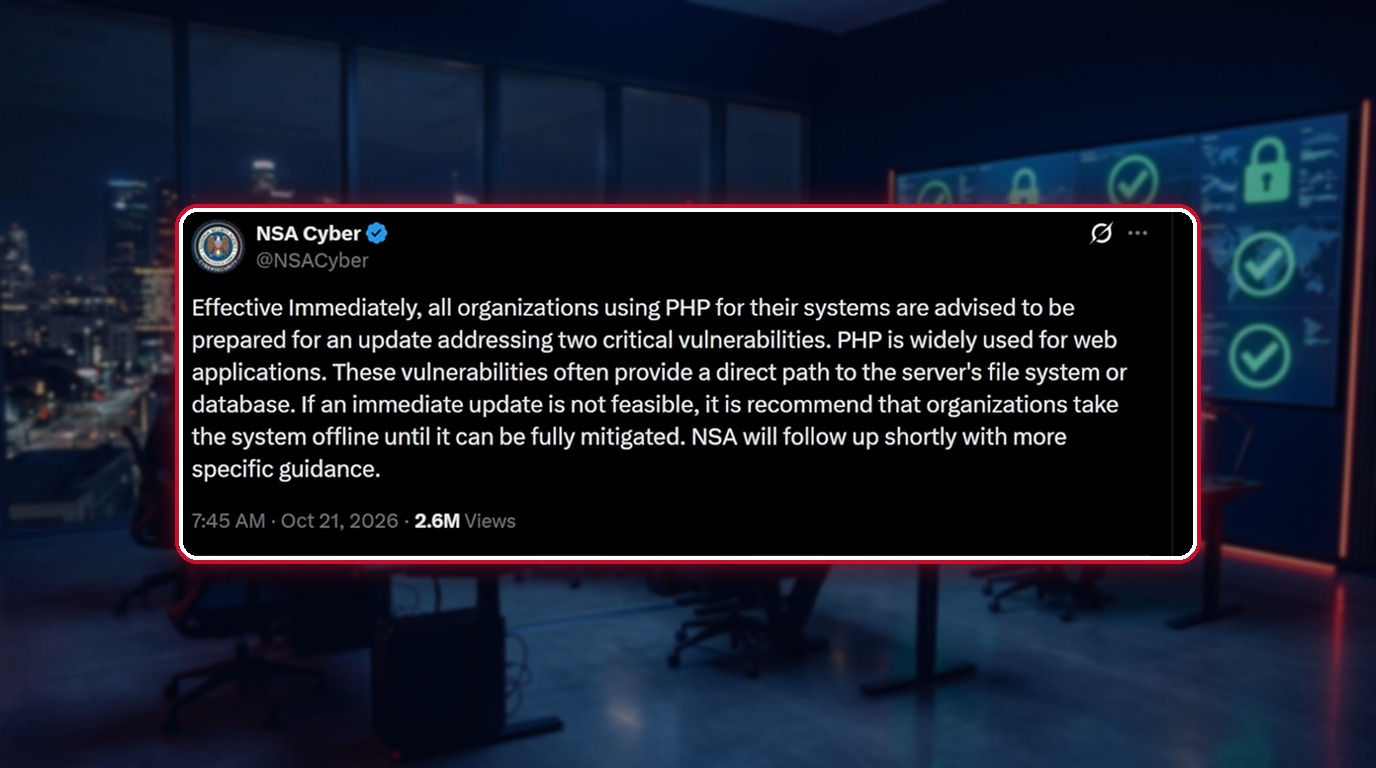
The NSA’s cybersecurity team urged every organization using PHP to prepare for an emergency update and, if it could not update immediately, to take its systems offline. For many organizations that meant a hard choice: patch fast or go dark.
We follow the biggest security agencies and act immediately. The security patch was in place within hours of the threat being announced, and not one of our websites went offline. Our servers install critical security fixes automatically, so the fix was already running by 2:30 a.m. Eastern time on October 22, before the East Coast woke up. That same morning our team checked every system by hand and patched the rest. Every server that runs our websites or holds our clients’ orders and documents is protected.
Because attackers were active before the fix existed, we did not stop at the patch. We inspected our servers for any trace of a break-in (altered files, hidden scripts, unknown programs, unexpected access keys) and found none. Challenge resolved.
Every day, people across the United States trust us with birth certificates, passports, diplomas, court papers and medical records for immigration, school and legal matters. Keeping that information safe is part of our job, and we take it seriously. Your orders and your documents are safe with us.
We are protected. Our clients are protected.
Questions about how we protect your documents? Call or text us toll free 24/7 at (844) 844-4423.